Andrew Curran
@AndrewCurran_
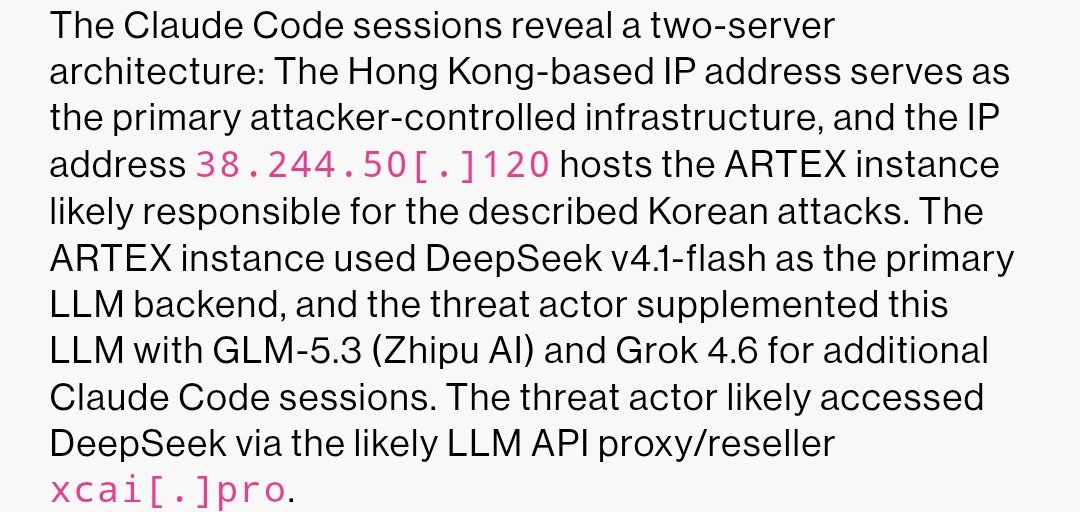
Last week some of South Korea's biggest banks were hit by a cyberattack. Thanks to a report from CrowdStrike tonight, we now know the entire hack may have been done by a single person. He used a combined stack of an open-source AI penetration tool named ARTEX, DeepSeek v4.1-Flash, GLM-5.3, Grok 4.6, and Claude Code.
8:14 AM UTC · Oct 8, 2026 · 1.3M Views
1585644.8K2.5K
Andrew Curran
@AndrewCurran_
crowdstrike.com
Unknown Threat Actor Uses AI-Driven ARTEX to Target South Korean Finance
CrowdStrike Intelligence identified infrastructure associated with a targeted campaign against South Korean financial institutions that resulted in exfiltrated data.
8:14 AM UTC · Oct 8, 2026 · 114.5K Views
415245121
Andrew Curran
@AndrewCurran_
Nathan Lambert:
Nathan Lambert @natolambert
The South Korean bank hack fits with this. Yes, open models are being fitted to be used by some attackers, but so long as Claude Code can be the orchestrator of a hack we desperately need open models to diffuse defense as well. A hard balance societally to stomach, but needed.
3:36 PM UTC · Oct 8, 2026 · 28K Views
13739