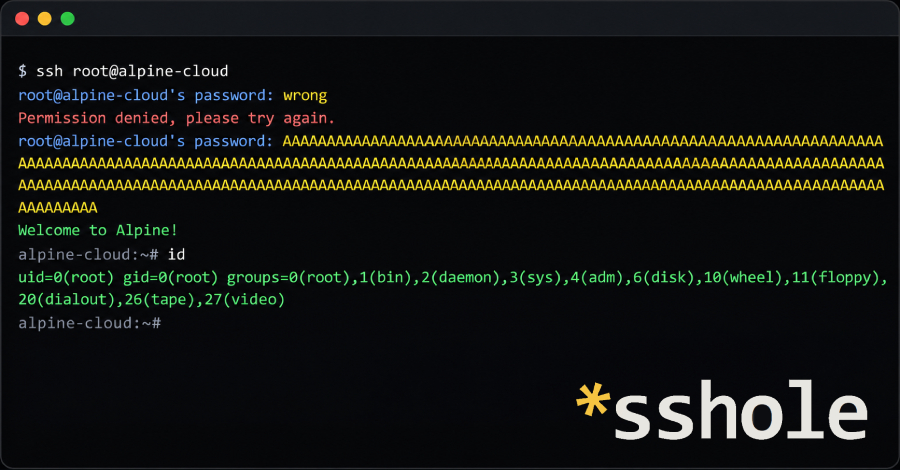
‼️WARNING - OpenSSH issues emergency fix for a critical SSH authentication bypass on Alpine Linux.
A password longer than 256 bytes can unlock key-only accounts on affected servers, without knowing the actual credentials.
Here's how it works ↓ thehackernews.com/2026/11/openss…
The Hacker News
@TheHackersNews
thehackernews.com
OpenSSH Issues Emergency Fix for Flaw Letting Long Passwords Bypass SSH Auth on Alpine Linux
OpenSSH 10.6p2 fixes a critical password bypass allowing access to key-only accounts on affected Alpine Linux servers using long passwords.
3:32 PM UTC · Nov 5, 2026 · 488.2K Views
805582.7K875
The Hacker News
@TheHackersNews
Here's the strange part:
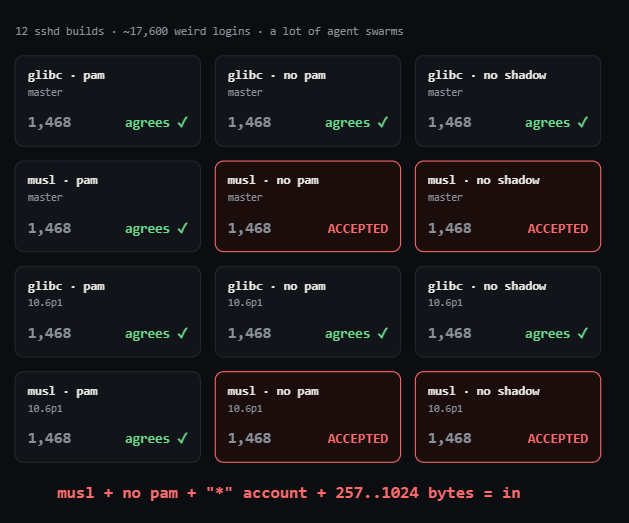
On affected Alpine Linux servers, SSH rejects a wrong password but can accept ANY password between 257 and 1,024 bytes for an account with no password set.
One long string is enough. No brute force needed.
On affected Alpine Linux servers, SSH rejects a wrong password but can accept ANY password between 257 and 1,024 bytes for an account with no password set.
One long string is enough. No brute force needed.
3:35 PM UTC · Nov 5, 2026 · 26.8K Views
31410122
The Hacker News
@TheHackersNews
Not every Alpine Linux server is vulnerable.
The bypass requires:
• SSH password logins enabled
• Password checks without PAM
• An account with no password set
• Another account with a compatible password hash
Key-only accounts can be exposed too.
The bypass requires:
• SSH password logins enabled
• Password checks without PAM
• An account with no password set
• Another account with a compatible password hash
Key-only accounts can be exposed too.
3:35 PM UTC · Nov 5, 2026 · 20.1K Views
1125916
The Hacker News
@TheHackersNews
It gets worse on certain Alpine cloud images.
The alpine user has passwordless doas access. If the SSH bypass conditions are met, an attacker can log in as alpine and become root.
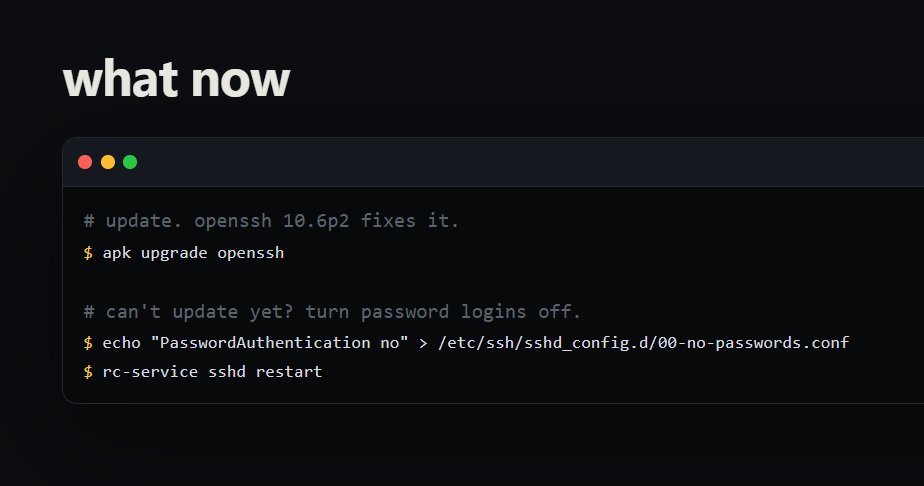
OpenSSH and Alpine have released fixes.
Can't update yet? Set PasswordAuthentication no and restart sshd.
The alpine user has passwordless doas access. If the SSH bypass conditions are met, an attacker can log in as alpine and become root.
OpenSSH and Alpine have released fixes.
Can't update yet? Set PasswordAuthentication no and restart sshd.
3:37 PM UTC · Nov 5, 2026 · 14.6K Views
06253